
Beyond the Alert: A Pragmatic Roadmap to Cloud Security Maturity Model (CSMM)
Cloud security has a fundamental structural problem, and most organizations are only beginning to fully recognize it. Despite significant investment in tooling and talent, security teams remain perpetually reactive, identifying misconfigurations after they have already reached production, triaging growing volumes of alerts, and working to remediate risks that have already existed in a potentially exploitable state, following the CSMM Model can change things around.


Executive Summary
This reactive cycle creates a persistent exposure window. No matter how quickly teams detect and respond, the underlying model assumes that risk will exist in the environment before it can be addressed.
In conversations with Ron Arbel, CEO of Aryon Security, a consistent theme emerges: the core problem in cloud security is not visibility, but timing. By the time a misconfiguration is detected, it has already existed in a potentially exploitable state.
The logical solution is to move security controls earlier - proactive, preemptive enforcement at the point where infrastructure changes are made.
This shift in timing represents more than an incremental improvement. It reflects a deeper evolution in how mature organizations approach cloud security: moving from detection and remediation toward prevention and enforcement.
But making this transition requires more than better tools. It requires a framework to guide the journey.
The Limits of the Detect-and-Remediate Model
For more than a decade, cloud security has been dominated by detection-centric approaches. Cloud Security Posture Management (CSPM) platforms, configuration scanners, and risk graphing tools have dramatically improved organizations’ ability to identify and prioritize misconfigurations.
These capabilities are valuable. They provide visibility, context, and prioritization - all essential components of modern security programs.
But they do not eliminate the fundamental constraint of reactive security: risk must first be introduced before it can be detected. A proactive, prevention-first model eliminates this constraint entirely by stopping risks before they ever materialize.
The implications are not theoretical. In December 2024, a cloud misconfiguration exposed sensitive data belonging to approximately 800,000 electric vehicle owners associated with Volkswagen. The misconfiguration itself was not inherently sophisticated - but the delay between its introduction and its discovery created a meaningful exposure window.
This pattern is common. In a reactive model, exposure window equals time-to-detection plus time-to-remediation. Even highly capable teams operating best-in-class detection tools cannot reduce that window to zero, because detection necessarily follows deployment.
Closing that gap requires shifting security earlier in the infrastructure lifecycle.
Why Maturity Requires a Strategic Framework
Technology alone does not create security maturity. Organizations need a structured way to assess their current capabilities, identify meaningful gaps, and prioritize improvements based on risk and operational context.
The Cloud Security Maturity Model (CSMM 2.0), developed collaboratively by the Cloud Security Alliance, Securosis, and IANS Research, provides such a framework.
The CSMM organizes cloud security into twelve capability areas across three domains:
- Foundational Domain - Identity and Access Management, account architecture, monitoring, and incident response - the core structural elements of any cloud environment.
- Structural Domain - Network security, workload protection, application security, and data protection - the technical controls that protect infrastructure and workloads.
- Procedural Domain - Risk management, DevOps integration, and governance - the operational and organizational processes that ensure security practices are consistently applied.
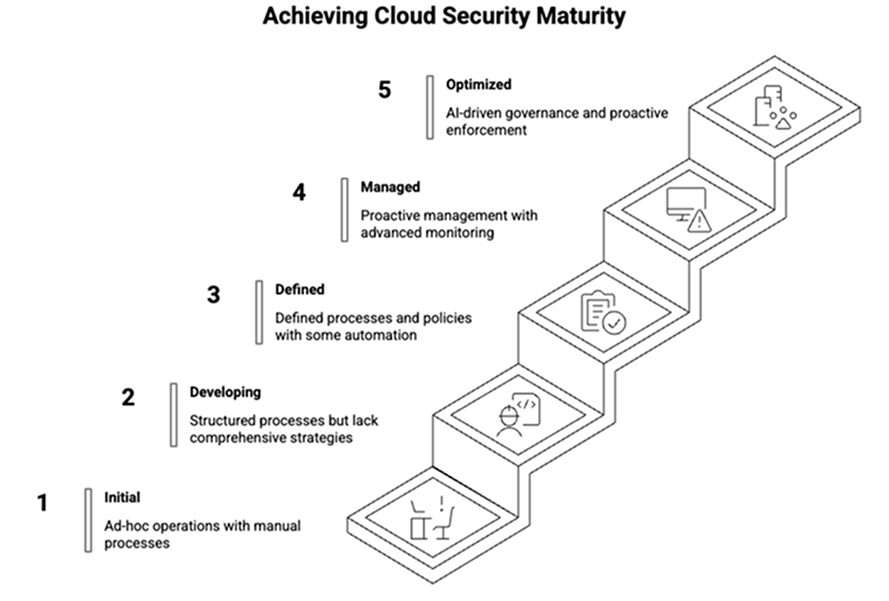
Across these domains, the model defines five maturity levels, ranging from Level 1 (Initial) to Level 5 (Optimized).
At lower maturity levels, security is largely manual, reactive, and fragmented. At higher maturity levels, security becomes automated, integrated into infrastructure workflows, and increasingly proactive and preventive in nature.
Many organizations remain concentrated in Levels 1 and 2, where detection and remediation dominate operational activity. Progressing beyond these stages requires shifting from alert-driven workflows to policy-driven guardrails.
Making the CSMM Actionable: Four Practical Applications
Used effectively, the CSMM is not merely an assessment tool, but a strategic instrument for guiding investment and operational change.
1. Establish an honest baseline
Organizations often have uneven maturity across capability areas. It is common to see relatively strong network controls alongside weaker identity governance or inconsistent policy enforcement. A structured assessment provides clarity on where risk is most likely to originate.
2. Build a roadmap aligned with business risk
Not every organization requires the same maturity level across all domains. The objective is not uniform optimization, but alignment between security capabilities and organizational risk tolerance, regulatory exposure, and operational scale.
3. Prioritize investments based on proactive structural risk reduction
Security budgets are finite. Maturity models help shift investment decisions from reactive tool acquisition toward structural risk reduction - prioritizing capabilities that prevent risk rather than simply improving visibility into it.
4. Communicate effectively with executive leadership
Maturity models provide a common language for communicating risk to boards and executive teams. Rather than reporting on operational metrics such as alert volume, security leaders can articulate progress in terms of structural capability improvements and reduced exposure.
The Shift Toward Enforcement-First Security
Reaching higher levels of maturity ultimately requires embedding proactive security directly into the infrastructure lifecycle itself.
Historically, security controls have operated primarily as observation layers - monitoring deployed environments and identifying deviations from expected configurations. While effective for detection, this model does not prevent risk from entering the environment.
A more mature approach introduces enforcement at the point where infrastructure changes are created and applied.
In this model, infrastructure configurations are evaluated against defined policies with preemptive enforcement before deployment. Changes that violate policy can be flagged, corrected, or blocked automatically, ensuring that unsafe configurations do not reach production environments.
This fundamentally changes the security operating model.
Security becomes a property of how infrastructure is deployed, rather than a function that evaluates it after the fact.
Developers receive immediate feedback when configurations violate policy, enabling correction before deployment. Security teams shift focus from triaging alerts toward defining preventive controls and governance frameworks. Operational overhead associated with reactive remediation declines.
Importantly, detection capabilities remain necessary. No preventive system is perfect, and runtime visibility continues to play a critical role in identifying novel threats, privilege abuse, or unintended behavior. But preventive enforcement reduces the volume of preventable risk entering the environment in the first place, strengthening the overall security posture.
This progression aligns closely with CSMM Level 5 maturity, where automation, integrated governance, and proactive control become foundational characteristics rather than aspirational goals.
Accelerating Maturity: Why Build vs. Adopt Is a Strategic Decision
One of the most common misconceptions about cloud security maturity is that it must be achieved entirely through internal effort - building custom guardrails, integrating policy engines, and incrementally evolving processes over time.
While this approach is possible, it is often slow, expensive, and difficult to sustain.
Reaching higher maturity levels - particularly Levels 4 and 5 in the CSMM - requires capabilities such as automated policy enforcement, integrated governance across infrastructure workflows, and consistent preventive controls across complex cloud environments. Developing these capabilities internally typically involves significant engineering investment, operational overhead, and ongoing maintenance.
For many organizations, adopting purpose-built third-party platforms can dramatically accelerate this progression.
These platforms embed proactive preventive controls, policy enforcement mechanisms, and governance capabilities directly into cloud operations, allowing organizations to implement mature security practices without building the underlying infrastructure themselves. Instead of developing custom tooling and processes over multiple years, organizations can adopt capabilities that align with higher maturity levels much earlier in their cloud journey.
This acceleration has two important implications.
First, it reduces the time required to reach higher levels of maturity. Exposure windows shrink sooner, and organizations benefit earlier from preventive controls that reduce the introduction of risk.
Second, it significantly lowers the total cost of achieving and sustaining maturity. Rather than allocating scarce engineering and security resources to building and maintaining internal security infrastructure, teams can focus on defining policies, improving governance, and addressing higher-order security challenges.
This shift changes the economics of cloud security maturity. Progression no longer depends solely on internal development cycles. Instead, organizations can leverage external platforms to operationalize mature security practices efficiently and at scale.
As a result, the maturity curve becomes less constrained by internal resource limitations and more aligned with strategic intent.

The Strategic Implications for Security Leaders
Cloud security maturity is not achieved simply by improving detection speed or adding additional monitoring layers. It requires a structural shift in where and how security controls operate.
Organizations that continue to rely primarily on detection-centric models will remain constrained by exposure windows inherent to reactive security.
Organizations that embed preventive guardrails into their infrastructure lifecycle fundamentally change this equation. They reduce the introduction of preventable risk, improve operational efficiency, and build a more resilient foundation for long-term cloud adoption.
This transition does not occur overnight. It requires clear assessment, deliberate planning, and investment aligned with maturity objectives.
But the direction is clear.
Cloud security is evolving from a model centered on finding problems to one centered on preventing them.
Frameworks like the CSMM provide the roadmap. Enforcement-centric approaches provide the operational mechanism. Together, they offer a pragmatic path forward for organizations seeking to move beyond reactive security and toward durable, scalable cloud protection.

Frequently Asked Questions
Notes & Sources
- Volkswagen breach (December 2024, ~800,000 EV owners) source: Dark Reading
- Electrek confirms the ~466,000 vehicles with precise location data and the "misconfigured Amazon cloud storage… for months"
- Securosis (co-author of the model) announcing CSMM 2.0
- IANS Research official CSMM
- The original 2020 CSMM launch release
- A guide to CSPM
Continue reading
The Key That Should Not Have Worked
A leaked cloud credential is usually treated as a detection problem. Find it, revoke it, rotate it, and move on. But the Volkswagen and Cariad data exposure raises a more important question: why was there a long-lived credential worth stealing in the first place? When a single reusable key can unlock sensitive cloud data, the leak is only part of the problem - the configuration that allowed that key to exist is the other.
The Role That Should Never Have Existed
On 29 July 2019, Capital One disclosed that an attacker had taken data relating to roughly 106 million people across the United States and Canada. The attacker was Paige Thompson, a former Amazon Web Services engineer, who was arrested the same day and convicted on computer fraud charges in June 2022. The company's settlements reached around $190 million.
Exploiting Cloud Misconfigurations: How Attackers Find Cloud Attack Paths (Part 1 - The Basics)
Cloud attacks don’t always begin with a vulnerability. Often, they begin with a misconfiguration that gives an attacker a path in. In Part 1 of this series, we look at cloud environments from the attacker’s perspective and break down the three conditions behind many exploitable cloud attack paths: Resource DIscovery, Network Accessibility, and Identity-Based Access.
Five Reasons Your Cloud Security Solution Is Failing You
Your cloud security tools may be working exactly as designed. That’s the problem.
Security teams are still finding and fixing the same misconfigurations over and over. The issue isn’t the tools-it’s a reactive model that detects risk after it already exists. Here are five signs that model has reached its limit.
50 Ways to Break Production - Why Cloud Security Remediation Is Harder Than It Looks
Cloud remediation is rarely as simple as changing a setting. Fixes can break production, require architectural changes or migrations, and conflict with IaC ownership. Prevention takes a different path: enforce the right configuration before deployment, while the resource is still cheap and safe to change. This article explores the challenges of remediating issues safely and effectively, and highlights what teams need to consider when remediation is unavoidable.
Cloud ShutterGap: Millions of Cloud Resources Exposed - The Blind Spot CSPM/CNAPP Tools Don’t Cover
Aryon's research reveals millions of misconfigured ephemeral cloud resources, publicly exposed for only moments before being removed. Often, these exposures last only a few minutes, long enough for attackers to discover and exploit them, but too short for traditional CSPM and CNAPP tools to detect. Many of these resources contain highly sensitive information.