Join the Front Line of Security
We’re Making it Possible for Everyone to Proactively Secure Complex Cloud Environments.
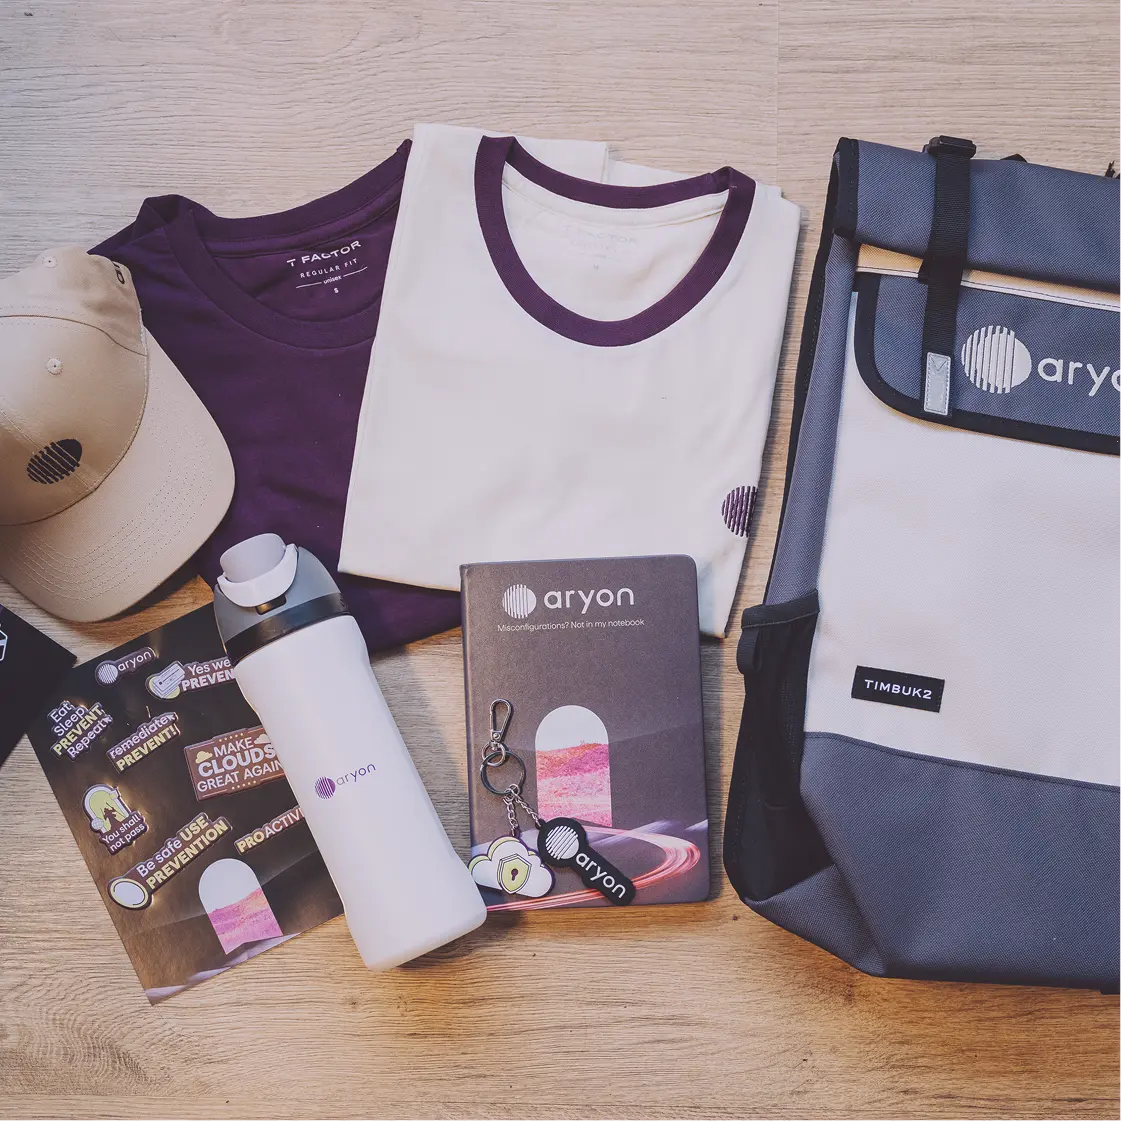
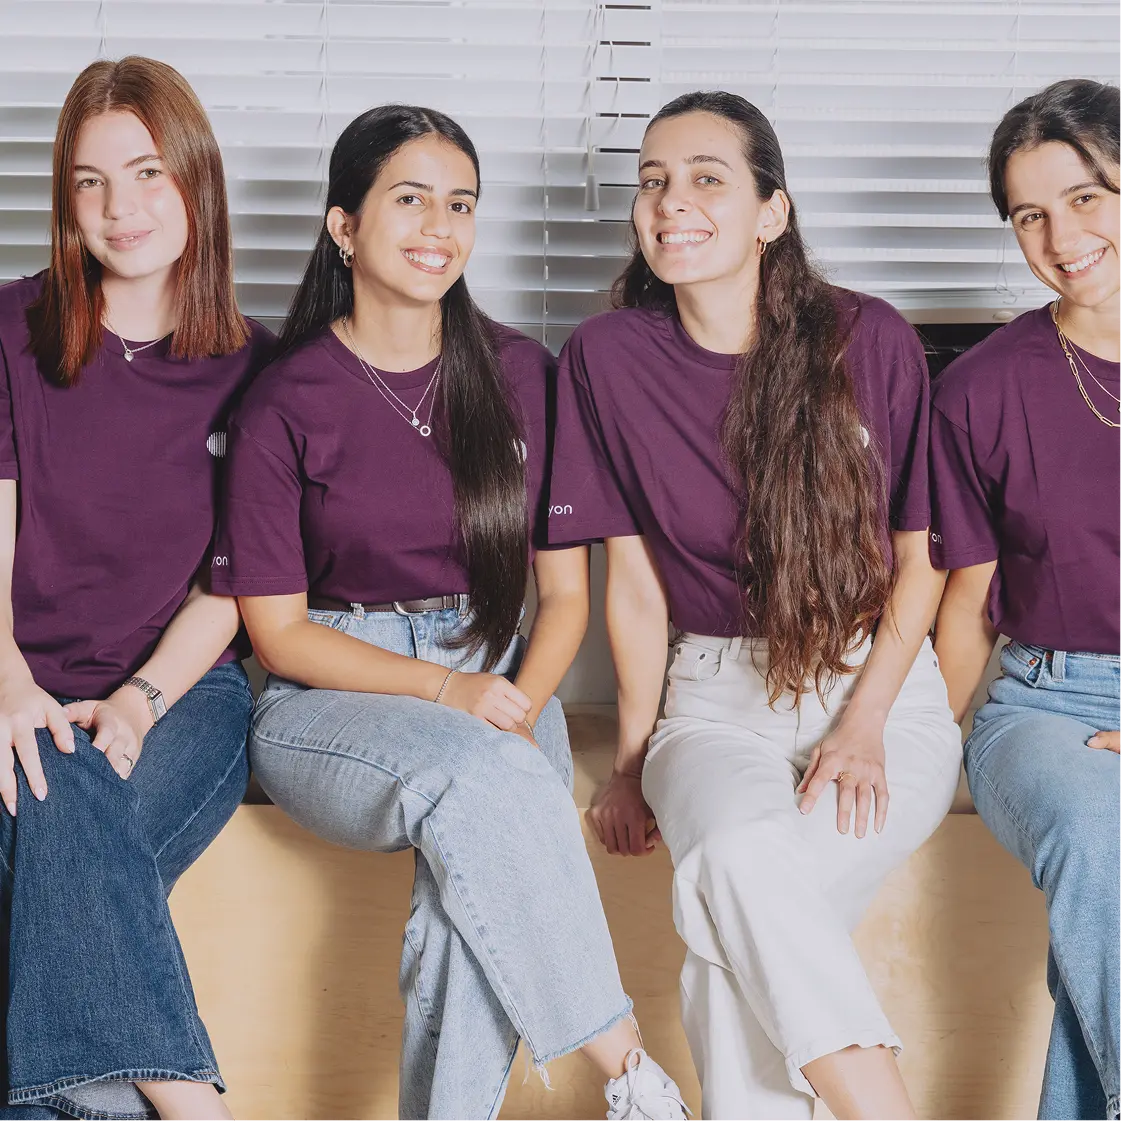
Aryon’s Values
We believe in people-driven technology. Passion and collaboration are a fundamental building block in every step of our journey.
Building talents & Safer clouds
Progress powered by people
Many minds. One force
Solving complex challenges
Job Openings

Look for us in the newspapers...
Read all about Aryon and our journey
Exploiting Cloud Misconfigurations, Part 2: How Attackers Discover Cloud Resources
The first thing an attacker needs is a target, so an attack naturally begins with resource discovery. During discovery, the attacker builds and expands a database of resource identifiers. These resources are then checked periodically for exploitable conditions. A resource may be discovered long before an opportunity to exploit it arises.
Ten Years Is a Long Time to Be Wrong
For nearly a decade, a cloud misconfiguration at Toyota left sensitive vehicle data belonging to approximately 2.15 million customers accessible from the internet. What began as a single configuration mistake in 2013 went undetected until 2023, exposing a fundamental weakness in traditional cloud security: detecting misconfigurations only works when someone is looking. And when Toyota finally investigated, it uncovered additional exposures. The incident raises a critical question for every organization operating in the cloud: Why wait to discover a security risk when you could prevent it from existing in the first place?
The Key That Should Not Have Worked
A leaked cloud credential is usually treated as a detection problem. Find it, revoke it, rotate it, and move on. But the Volkswagen and Cariad data exposure raises a more important question: why was there a long-lived credential worth stealing in the first place? When a single reusable key can unlock sensitive cloud data, the leak is only part of the problem - the configuration that allowed that key to exist is the other.